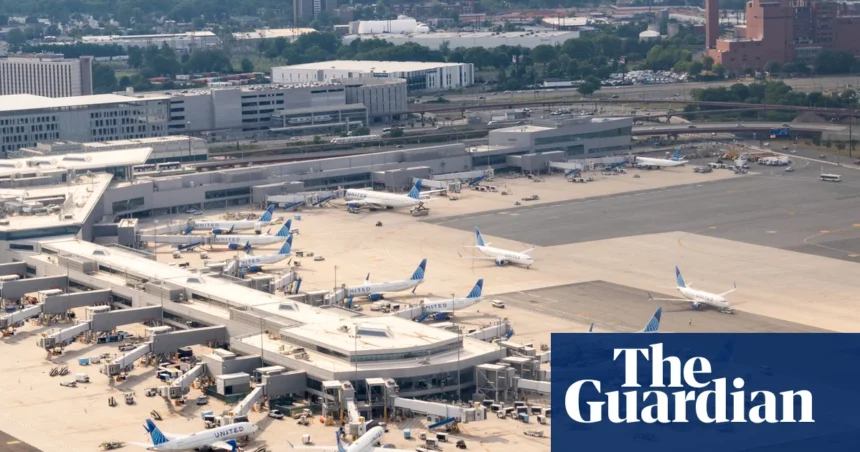
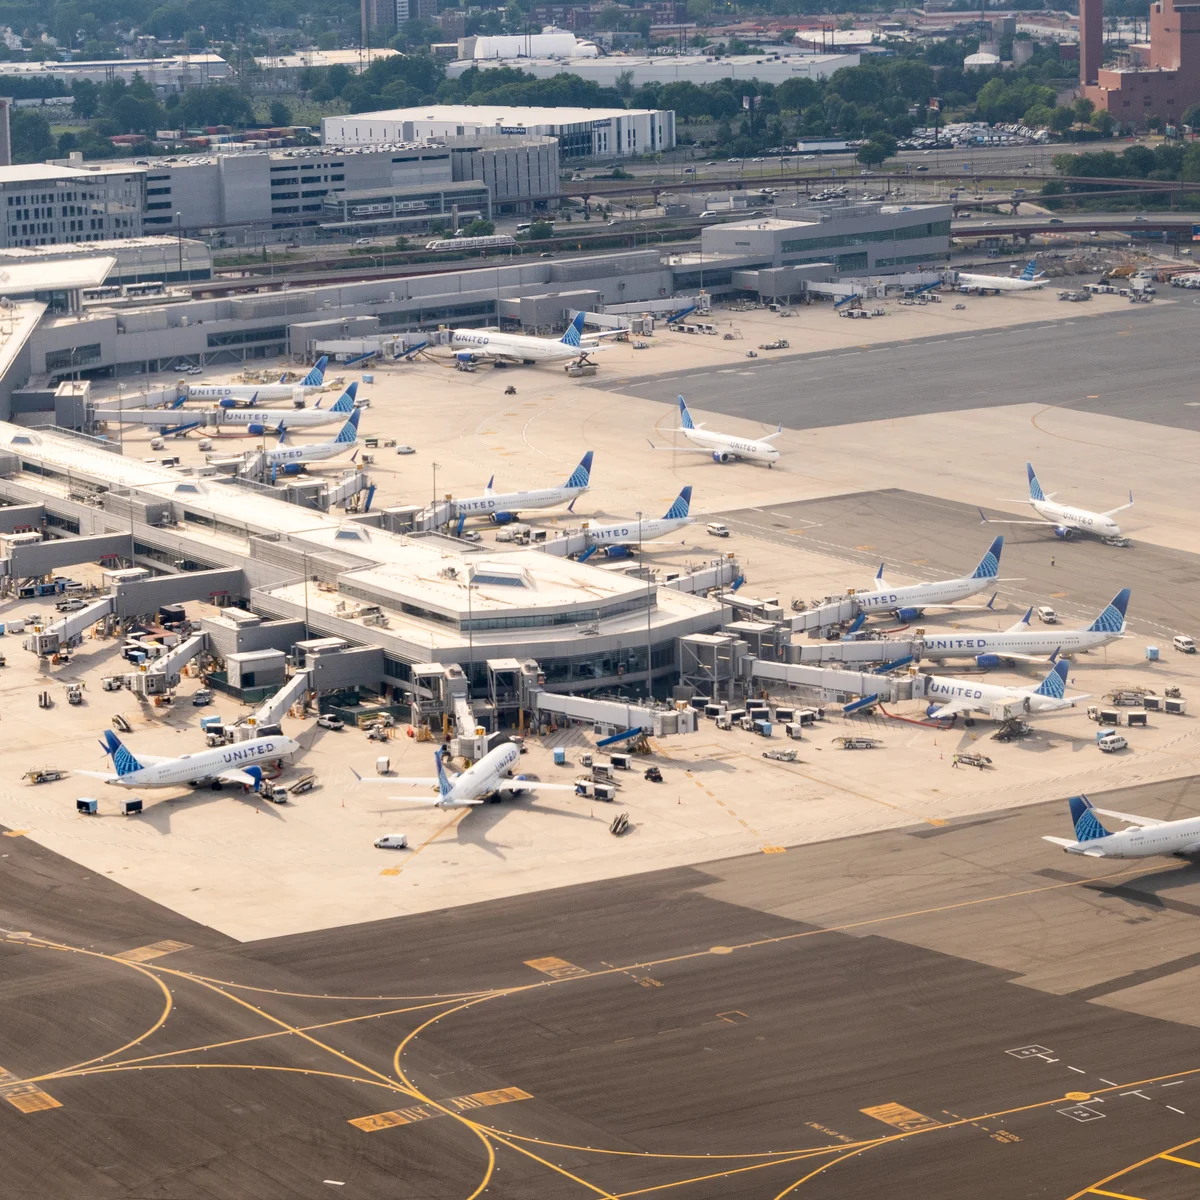
The Federal Aviation Administration (FAA) imposed a ground stop on Newark Liberty International, Philadelphia International, and Teterboro airports on Monday morning, halting arrivals and departures at approximately 10am as radio frequency equipment at the Philadelphia terminal radicont was compromised. The disruption, affecting over 44,000 daily flights that traverse these hubs, underscores escalating cybersecurity threats confronting the nation’s most critical aerial corridors. Authorities have not disclosed the root cause of the outage, leaving crews scrambling amid escalating delays.
Operational Disruption and Immediate Impact
The FAA’s decision to halt operations stemmed from compromised radio frequencies at the Philadelphia Terminal Radar Approach Control (Tracon) facility. This technical fault rendered real-time coordination between controllers and aircraft impossible until the early afternoon, forcing all movement at Newark, Philadelphia, and Teterboro into standstill. Arrivals and departures were scrambled, with passengers stranded awaiting alternative routes. The agency has remained tight-lipped regarding the precise malfunction, though its nature suggests a sophisticated electronic interference rather than mechanical failure. For commercial operators reliant on seamless transcontinental connections, the ripple effects are immediate: cargo shipments face bottlenecks, connecting flights are derailed, and passengers endure hours of uncertainty. The scale of the incident reflects broader vulnerabilities within the national airspace management network, where reliance on legacy infrastructure persists despite mounting evidence of systemic fragility.
The Security Crisis Exposed by Government Audit
Concurrent with the operational turmoil, the Government Accountability Office (GAO) delivered a damning report that frames the current crisis as emblematic of deeper institutional neglect. The audit revealed that the FAA had failed to complete risk assessments for seven of eight reviewed communication systems, leaving critical gaps in defence against emerging threats. Specifically, two messaging platforms historically deployed at the Philadelphia base suffer from antiquated design, predating contemporary cybersecurity norms and omitting essential safeguards such as encryption. These deficiencies render the networks susceptible to malicious actors capable of injecting false clearance commands, fabricating flight bans, or even commandeering aircraft mid-flight.
Senator Ron Wyden of Oregon, whose career has been defined by advocacy on surveillance and digital privacy, articulated stark warnings. He labelled the FAA’s lax stance on secure communications a “major threat” to national security, economic stability, and public aviation safety. “The FAA needs to issue new standards, as soon as possible, to protect the security of airline communications,” he declared. The GAO further highlighted that the agency lacks a unified real‑time detection mechanism for interference, jamming, and spoofing attempts—capabilities deemed indispensable for preemptive countermeasures. Such lapses invite not merely inconvenience but catastrophic consequences, from cascade failures in air traffic management to weaponised disruptions targeting high‑value assets.
Policy Responses and Ongoing Risks
In response to the GAO’s indictment, the Department of Transportation affirmed alignment with the watchdog’s nine recommendations. These include mandating comprehensive risk assessments across all aviation systems, instituting continuous monitoring capabilities for signal manipulation, and establishing formal protocols for information sharing among federal, state, and private entities. While the proposed reforms represent a necessary evolution in regulatory posture, critics argue they arrive too late to prevent imminent crises. The historical record offers cautionary parallels: earlier this year, an outage at Newark’s radar approach control disrupted departures for several minutes, prompting the FAA to migrate the centre to redundant fibre‑optic pathways—a costly interim fix designed to mitigate future recurrence. Yet such ad‑hoc adjustments underscore a troubling trend, where reactive patches instead of proactive investment become the norm. The persistence of unpatched vulnerabilities in legacy systems signals a broader cultural complacency within the sector, wherein outdated technologies remain entrenched under the guise of operational continuity.
Broader Implications for National Security and Economy
Beyond the immediate chaos at these three hubs, the situation casts a wide net over the United States’ aviation ecosystem. With over 3 million passengers processed annually through the network served by Newark, Philadelphia, and Teterboro, any disruption translates directly into billions in lost revenue for airlines, logistics firms, and ancillary services. More alarmingly, the GAO’s report warns that adversaries—both state‑sponsored groups and opportunistic hackers—can exploit these gaps to conduct geographically dispersed attacks on critical infrastructure. Recent incidents involving Estonia and Finland, where Russian actors accused of interfering with satellite navigation raised suspicions of broader European vulnerability, lend weight to concerns about coordinated interference campaigns. The convergence of technological naivety and strategic oversight elevates this episode beyond a mere logistical hiccup, framing it as a potential flashpoint in the nation’s struggle to safeguard its skies against invisible enemies. Without decisive action, the spectre of cascading failures looms larger than ever.
Why it Matters
The current ground stop sequence exemplifies how deteriorating cybersecurity fundamentals can rapidly erode the backbone of a nation’s mobility and security apparatus. When fundamental infrastructure fails, the ramifications extend far beyond individual travellers—they reverberate through supply chains, trade flows, and national resilience. By exposing the inadequacy of existing protective frameworks, the GAO report forces stakeholders to confront the reality that today’s aeronautical networks are increasingly exposed to malicious exploitation. Addressing these vulnerabilities is not simply a matter of technical refinement; it is a prerequisite for preserving economic vitality, upholding public trust, and deterring hostile interference that could undermine both civilian comfort and strategic autonomy. The stakes, therefore, cannot be overstated—inaction risks transforming routine operational hiccups into systemic crises capable of destabilising entire sectors.