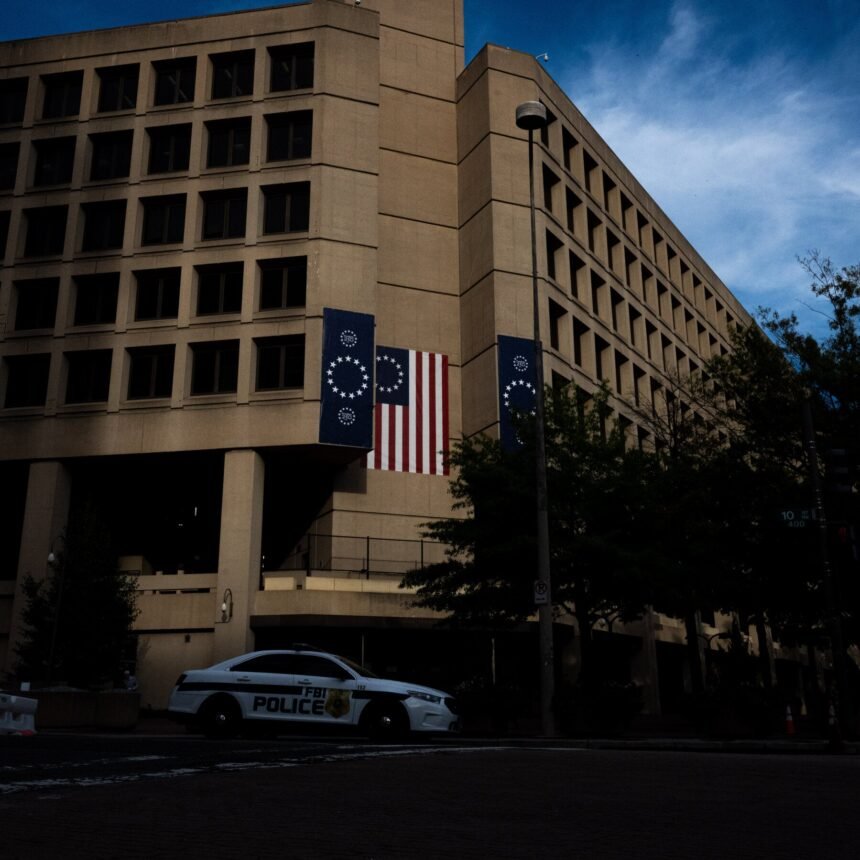
The Federal Bureau of Investigation has taken a significant step in its ongoing battle against cyber‑crime by apprehending a central figure linked to the ShinyHunters collective, a group notorious for targeting sensitive government databases. The operation follows a breach that compromised the personal records of numerous FBI agents, prompting an urgent internal review and a broader reassessment of cybersecurity protocols across the law‑enforcement community.
The Nature of the Breach
ShinyHunters first surfaced on underground forums in early 2022, quickly gaining a reputation for infiltrating poorly defended networks and exfiltrating large volumes of data. The most recent incident, which came to light in late 2023, saw the group gain unauthorised access to an FBI internal repository that contained personally identifiable information (PII) of active agents, including home addresses, phone numbers and, in some cases, financial details. The breach was discovered through routine anomaly detection alerts, leading to a coordinated response that isolated the compromised systems and launched a forensic investigation.
According to FBI officials, the intrusion exploited a combination of outdated software and weak credential management within a peripheral bureau’s IT infrastructure. The agency’s cyber‑division emphasised that the compromised data did not include classified operational files, but the exposure of agents’ personal information raised serious safety and privacy concerns. “We treat any compromise of our personnel’s data as a serious matter,” said the bureau’s director during a press briefing, stressing the need for heightened vigilance.
The Arrest and Ongoing Investigation
The individual apprehended, identified only as a 32‑year‑old male from the mid‑west, was taken into custody without incident in a coordinated operation involving the FBI’s Cyber Division, the Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency (CISA), and several state law‑enforcement partners. While the suspect has not yet been formally charged, court documents indicate he was arrested on suspicion of unauthorised access to a protected computer and conspiracy to distribute stolen data.
Investigators have linked the suspect to a series of earlier attacks attributed to ShinyHunters, including breaches of local government networks and a prominent energy firm. The group’s modus operandi typically involves scanning for vulnerable web applications, exploiting default passwords, and then using the compromised systems as a staging ground for data exfiltration. The FBI’s cyber‑experts are currently analysing the seized digital evidence to determine the full scope of the operation and to identify any accomplices who may have assisted in the planning or execution of the breach.
Bipartisan Reaction in Congress
The breach has ignited a rare moment of bipartisan consensus on Capitol Hill, where lawmakers from both the Democratic and Republican parties have called for stricter oversight of federal cybersecurity practices. The Senate Judiciary Committee’s Subcommittee on Cybersecurity has scheduled a hearing for early next month, inviting testimony from FBI leadership, CISA director, and representatives from affected bureaus.
Senator Lisa Murkowski (R‑AK) and Senator Mark Warner (D‑VA), the subcommittee’s chairs, jointly issued a statement warning that “the exposure of law‑enforcement personnel’s personal data undermines operational security and erodes public confidence.” Their statement called for a comprehensive audit of IT infrastructure across all federal agencies, increased funding for cyber‑defence initiatives, and the potential introduction of new legislation to tighten data‑handling standards.
Similarly, the House Committee on Oversight and Reform has launched its own investigation, demanding documents from the FBI regarding the timeline of the breach, the extent of data loss, and the steps taken to mitigate the impact. Representative James Comer (R‑KY), the committee’s chair, has pledged “no stone will be left unturned” to ensure accountability and prevent future compromises.
Legislative Outlook and Policy Implications
The congressional focus has already sparked discussion of several proposed bills aimed at bolstering federal cybersecurity. One measure, the “Federal Personnel Data Protection Act,” seeks to establish uniform standards for storing and accessing personal information of government employees, with strict penalties for non‑compliance. Another, the “Cyber‑Threat Response Enhancement Act,” would expand the FBI’s authority to share threat intelligence with private sector partners and streamline the process for rapid incident response.
Industry groups and cybersecurity firms have expressed cautious optimism. The Information Technology Industry Council (ITI) welcomed the bipartisan push, noting that “the private sector stands ready to collaborate on best practices and technology solutions that can protect both government and citizen data.” However, some experts warn that legislative action must balance security needs with civil‑ liberties concerns, particularly as new powers could affect surveillance and data collection practices.
Why it Matters
The arrest of the ShinyHunters suspect marks a pivotal moment in the federal government’s fight against organised cyber‑crime, but its significance extends far beyond a single apprehension. The breach exposed a critical vulnerability within the very agency tasked with safeguarding national security, prompting an urgent re‑evaluation of how personal data of law‑enforcement officers is protected. Moreover, the unified bipartisan response signals a rare political consensus on the necessity of strengthening cyber‑defences, which could accelerate the passage of long‑stalled security legislation. As cyber‑threats continue to evolve, this case underscores the imperative for robust, coordinated defences and vigilant oversight to protect both government personnel and the public’s trust in institutions.