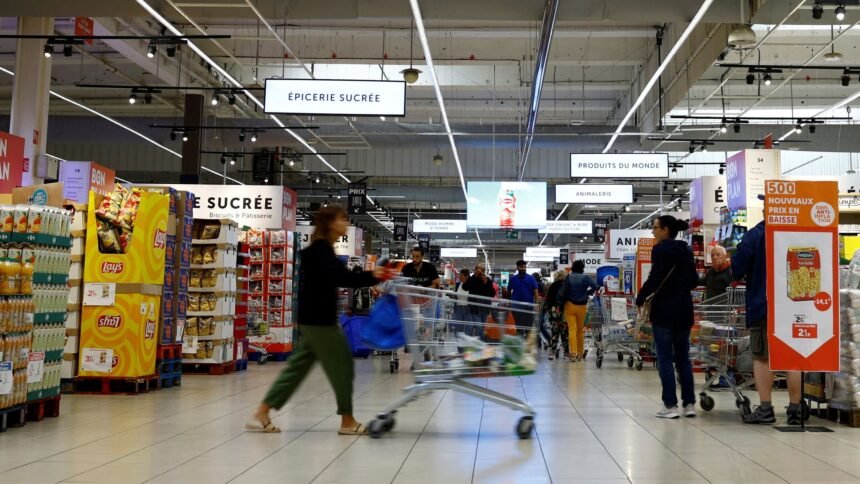
A coordinated cyber intrusion overnight disabled temperature controls across hundreds of French supermarket locations, driving commercial refrigeration units to 50°C and triggering multiple fires. The incident marks a dangerous escalation in attacks on critical civilian infrastructure, transforming food preservation systems into active safety hazards and raising urgent questions about the resilience of automated supply chains across Europe.
From Preservation to Combustion
The attack unfolded during the early hours when staffing levels were minimal. Malicious code infiltrated the centralised building management systems that govern refrigeration, heating, and ventilation across multiple retail sites. Instead of merely disabling cooling — a tactic seen in previous ransomware campaigns — the attackers actively reversed the thermal logic. Compressors were forced to operate as heaters. Defrost cycles were triggered continuously. Within hours, walk-in freezers and display cases designed to maintain sub-zero temperatures became ovens.
Fire brigades responded to alarms at over a dozen locations in the Île-de-France, Lyon, and Marseille regions. At three sites, the sustained heat ignited insulation materials and electrical wiring, causing structural damage that will keep those stores closed for weeks. No injuries have been reported, but the psychological impact on night-shift workers who encountered smoke-filled aisles is already drawing union scrutiny.
A New Playbook for Industrial Sabotage
Cybersecurity analysts describe the methodology as a significant departure from established threat models. “We’ve seen ransomware encrypt point-of-sale systems. We’ve seen wipers destroy logistics databases,” said Cédric Lévy, a senior researcher at ANSSI, France’s national cybersecurity agency. “This is the first confirmed case in Europe where operational technology was weaponised to create physical fire risk in a retail environment. The intent appears to be destruction, not extortion.”
The malware variant, preliminarily dubbed “Thermite” by French CERT analysts, exhibits modular architecture capable of targeting specific programmable logic controllers (PLCs) manufactured by two major European vendors. These controllers are widely deployed not only in supermarkets but in cold storage warehouses, pharmaceutical depots, and hospital blood banks. ANSSI has issued an emergency directive urging all facilities using the affected PLC models to disconnect them from corporate networks immediately and revert to manual temperature monitoring.
Supply Chain Cascades and Consumer Impact
The economic fallout extends far beyond the scorched aisles. Early estimates suggest €40–60 million in spoiled inventory — fresh produce, dairy, frozen proteins, and temperature-sensitive pharmaceuticals. Insurers are already signalling that policies covering “cyber-physical damage” may face contested claims, as most existing policies exclude losses arising from deliberate manipulation of industrial control systems.
For consumers, the disruption coincides with peak summer demand. Regional distribution centres are rerouting stock to unaffected stores, but logistics bottlenecks are inevitable. The French Retail Federation warns of localised shortages for up to ten days, particularly in perishable categories. Meanwhile, the Ministry of Agriculture has activated emergency food safety protocols, deploying mobile testing labs to verify that no compromised products entered the donation stream for food banks.
Vulnerabilities in the Connected Cold Chain
The incident exposes a systemic fragility that extends well beyond France. Across the Asia-Pacific region, where rapid digitalisation of cold chain logistics has outpaced security investment, similar architectures prevail. In Singapore, Japan, and Australia, major supermarket chains rely on identical European PLC platforms, often managed by third-party facilities contractors with remote access privileges. A 2023 audit by the Australian Cyber Security Centre found that 68% of food retail OT networks lacked network segmentation from corporate IT — a gap that would allow lateral movement identical to the French attack vector.
Singapore’s Cyber Security Agency has already convened an emergency briefing with major retailers. Japan’s METI is expected to issue revised guidelines for food infrastructure operators by week’s end. The lesson is clear: the convergence of IT and OT in perishable logistics has created a attack surface where a single compromised credential can spoil a nation’s dinner.
Why it Matters
This attack signals a paradigm shift — cybercrime has moved beyond data theft and financial extortion into the realm of kinetic sabotage against civilian sustenance infrastructure. When refrigeration becomes a weapon, the cold chain that feeds millions transforms into a vector for arson, waste, and public endangerment. For policymakers and security leaders across the Asia-Pacific and beyond, the French supermarket fires are not a distant cautionary tale; they are a proof of concept demanding immediate segmentation of operational technology, mandatory manual override capabilities, and a fundamental rethink of who holds the keys to the systems that keep our food safe.