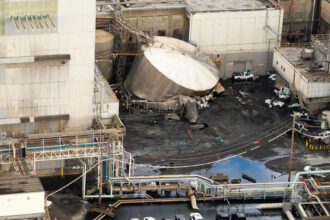
Lithuanian officials have concluded that a fire at a Starlink facility in the country was an act of sabotage rather than an accident. Although the blaze caused no serious damage to the network, the deliberate attack has raised fresh concerns about the security of infrastructure supporting satellite communications across Europe. Similar incidents involving the provider in Bulgaria and Poland have increased scrutiny of its facilities and the reliance of Ukraine’s armed forces on the service.
Official finding points to a deliberate attack
The Lithuanian assessment is significant because it places the incident within the category of deliberate disruption rather than ordinary infrastructure failure. A deliberate attack need not knock a satellite network offline to be consequential: even a contained fire can test security procedures, interrupt local operations and signal an interest in undermining a service with military value.
Officials said the fire did not seriously damage Starlink’s network. That limited immediate impact may reflect the redundancy built into the service, according to the broader picture of how satellite connectivity operates. It does not, however, remove the significance of the reported sabotage or the questions it raises about protection at ground-level sites.
Starlink, operated by SpaceX, relies on a combination of low-orbit satellites, ground stations and local infrastructure to provide broadband services. Disrupting a site in Lithuania would not necessarily disable the wider system, but it could affect local capacity, maintenance and the ability to restore service if other parts of the network came under pressure.
Incidents across three countries
The Lithuanian fire came after comparable incidents in Bulgaria and Poland involving the satellite internet provider. The geographical spread of the reported episodes has prompted concern that physical disruption of technology with defence applications may be becoming part of a wider campaign.
There is not yet enough public information to determine whether the incidents were coordinated, whether the same actor was responsible or whether each event served a separate purpose. Attribution of sabotage is more demanding than identifying an accident: investigators must establish intent, connect any available evidence and avoid reaching conclusions based solely on timing.
Even so, the sequence matters. A series of small incidents can be used to test security, divert police and intelligence resources or demonstrate reach. It can also force operators and governments to spend more on physical safeguards, redundancy and continuity plans. The absence of a major outage would therefore not mean that the events lacked strategic intent.
Starlink’s importance to Ukraine
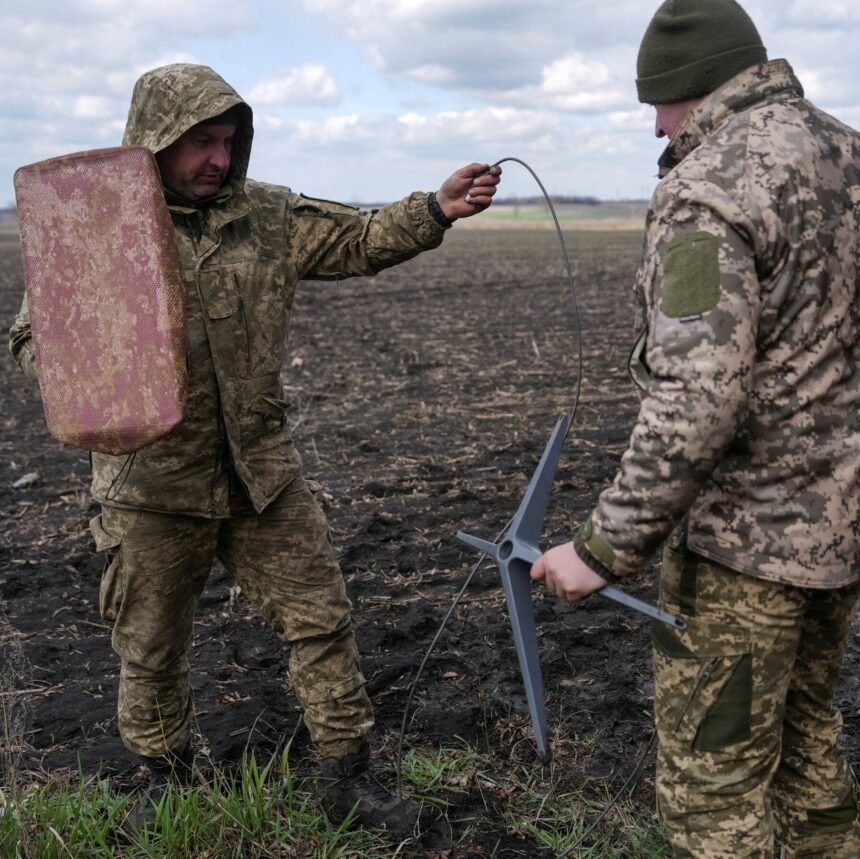
The provider has become central to Ukraine’s battlefield communications since Russia launched its full-scale invasion. Ukrainian forces have used Starlink terminals to maintain links across front lines, while civilians and public agencies have also relied on the service where conventional networks are damaged or unavailable.
That dual role has made the platform a prominent example of the changing relationship between commercial technology and state security. Supporters of the system credit it with providing rapid, flexible connectivity when traditional infrastructure is vulnerable. Critics counter that dependence on a private company creates strategic exposure, including questions over cost, control, cybersecurity and the availability of alternatives.
Those arguments are compatible. The value of a service does not remove the need to protect it, and the risks of reliance do not necessarily outweigh its operational benefits. Across political divides, the practical lesson is that rapid innovation should be matched by redundancy, contingency arrangements and clear lines of responsibility for critical communications.
What remains unclear
Key details remain outstanding. The available account does not identify the perpetrators, explain precisely how the fire was started or set out what evidence led Lithuanian authorities to classify it as sabotage. Nor has it established the operational consequences of the earlier incidents in Bulgaria and Poland.
Attention is therefore likely to focus on the forensic investigation, any arrests or surveillance material, and whether similar methods appear in other attacks. Operators, meanwhile, may need to reassess access controls, monitoring and emergency response at facilities considered relevant to network resilience.
For governments, the broader challenge is to determine how to protect infrastructure without allowing a limited disruption to become a major failure. Satellite connectivity offers an alternative to vulnerable cables and terrestrial networks, but its effectiveness ultimately depends on the security of the ground equipment, power supplies and fibre connections that link the space-based system to users.
Why it Matters
The Lithuanian fire may have produced little immediate disruption, but that is precisely what makes the incident worth taking seriously. If the recent cases form part of a coordinated campaign, their purpose may be