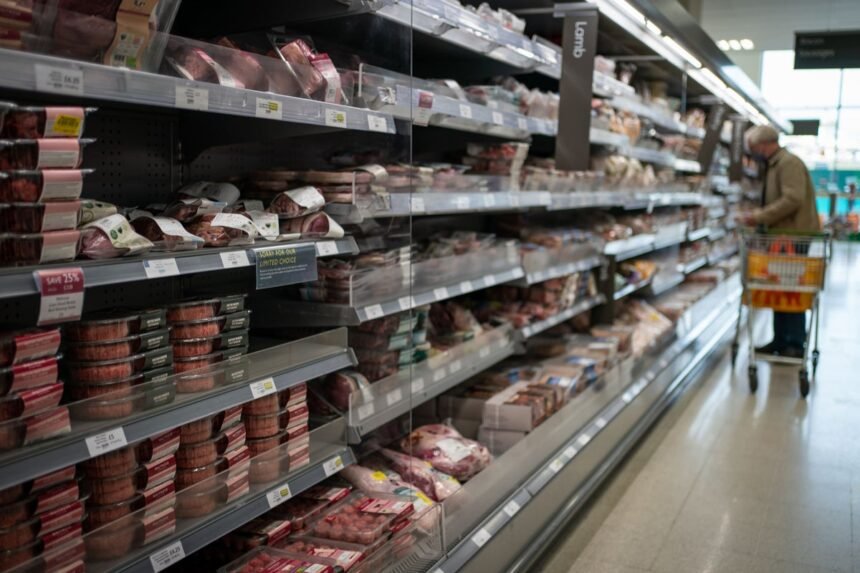
The National Cyber Security Centre (NCSC) confirmed it is liaising with a handful of British meat suppliers after a coordinated cyber incident affected refrigeration equipment across the continent. The disruption, which unfolded late on Monday, caused some cold‑storage units to malfunction, with temperatures rising as high as 100 °C in at least one case. However, the affected facilities were empty at the time, meaning no food products were compromised. The NCSC described the overall effect on the UK as “minimal”, while industry bodies stressed the need for heightened vigilance across the supply chain.
Supply chain disruption contained
A small group of members of the Association of Independent Meat Suppliers (Aims) reported unexpected failures in their cold‑storage systems. The trade group, which represents roughly 300 firms, said a few of its members became “collateral” in a broader attack that targeted software used by supermarkets and food distributors throughout Europe. In one instance, a refrigeration unit’s temperature spiked to 100 °C, while another saw its systems begin to defrost. Because the units were empty during the outage, no meat was lost. An Aims spokesperson emphasised that the incident serves as a reminder for all food‑industry operators that their systems can be seen as attractive targets, urging members and the wider sector to remain alert.
Industry and regulatory response
Paul Chichester, the NCSC’s Director of Operations, told an audience at the centre’s annual report launch that the agency is aware of the UK incidents and is working closely with the affected organisations. He stressed that the current impact is minimal and that the NCSC is actively identifying existing vulnerabilities within British firms, aiming to close them before they can be exploited. The agency’s incident‑management team has already contacted a handful of vulnerable organisations, according to Dr Richard Horne, the NCSC’s Head.

The British Retail Consortium’s assistant director of regulatory affairs, Graham Wynn, highlighted that retailers invest heavily in cyber‑security and are collaborating with the NCSC to reinforce the protection of refrigeration equipment. Rupert Ashby, chief executive of the British Frozen Food Federation, noted that retailers across the supply chain are treating cyber‑security as a top priority, reviewing freezer provisions and assessing system susceptibility.
Broader cyber‑security context
The NCSC’s annual report revealed that its incident‑management team received 1,831 reports of cyber attacks this year, of which 337 required active support and 80 were deemed nationally significant. The team also issued warnings to 8,500 organisations after detecting compromised systems. Dr Horne explained that the attack on French supermarket refrigeration units exploited legacy technology connected to the internet with default passwords, a vulnerability that has long been flagged by cyber‑security experts.
When asked about the Defence Secretary’s recent call for the public to consider stockpiling supplies, Dr Horne replied that such warnings are “absolutely” relevant, citing criminal attacks on UK retailers last year. He reiterated that while the NCSC alerts and intervenes where possible, ultimately each organisation bears responsibility for its own cyber‑defences.
What businesses need to know
Retailers and food‑supply firms are being urged to adopt a proactive stance. This includes regularly updating software, conducting thorough vulnerability assessments, and ensuring that contingency plans are in place to relocate perishable goods if systems fail. The incident underscores the interconnected nature of modern food‑distribution networks, where a breach in one part of the chain can ripple across borders.

The attack also highlights the lingering risks posed by outdated equipment. Many cold‑storage units, especially those installed several years ago, rely on internet connectivity for remote monitoring but lack robust security protocols. Experts recommend a phased approach: first, identify all internet‑connected devices; second, change default credentials and apply the latest firmware updates; and third, segment networks to isolate critical systems from less secure environments.
Industry analysts note that the event may prompt a review of procurement policies, with a greater emphasis on cyber‑resilient technology. Suppliers may need to factor in additional costs for secure refrigeration solutions, but the expense is likely to be outweighed by the avoidance of product loss and reputational damage.
Why it Matters
The episode reveals how cyber threats can directly impact the physical infrastructure that underpins food security, even if the immediate consequences appear limited. While the UK’s meat supply remained untouched, the incident demonstrates the fragility of systems that are increasingly reliant on networked technology. For businesses across the retail and logistics sectors, this serves as a stark reminder that cyber‑security is not merely an IT concern but a core component of operational resilience. As attackers continue to refine their methods, organisations that fail to invest in robust defences risk not only financial loss but also potential threats to public safety. The broader lesson is clear: proactive cyber‑risk management is essential to safeguard both economic stability and the everyday essentials that consumers rely on.